US Cybersecurity Directives 2026: 3-Month Compliance Guide for Businesses
Anúncios
Navigating the New US Cybersecurity Directives for 2026: A 3-Month Compliance Guide for Businesses
The landscape of cybersecurity is ever-evolving, and with the impending US Cybersecurity Directives for 2026, businesses across all sectors are facing a critical compliance deadline. This isn’t just another regulatory hurdle; it’s a fundamental shift towards a more resilient and secure digital infrastructure. For many organizations, the clock is ticking, and a proactive, strategic approach is essential. This comprehensive guide is designed to help businesses understand the new directives, outline a practical 3-month compliance roadmap, and implement the necessary changes to not only meet but exceed these new standards.
Anúncios
The urgency cannot be overstated. Non-compliance with these directives could lead to significant financial penalties, reputational damage, legal liabilities, and, most importantly, increased vulnerability to cyberattacks. A 3-month window might seem tight, but with focused effort and a clear strategy, your organization can achieve robust compliance. Our aim is to provide practical solutions and actionable steps, ensuring your business is well-prepared for the future of US Cybersecurity Compliance.
Understanding the Core of the 2026 US Cybersecurity Directives
Before diving into the compliance roadmap, it’s crucial to grasp the foundational principles and key changes introduced by the 2026 US Cybersecurity Directives. These directives aim to strengthen national cybersecurity infrastructure, protect critical data, and enhance incident response capabilities across industries. While specific details may vary depending on your sector (e.g., finance, healthcare, critical infrastructure), several overarching themes are consistent:
Anúncios
- Enhanced Risk Management Frameworks: A greater emphasis on identifying, assessing, and mitigating cyber risks systematically. This often means adopting or aligning with frameworks like NIST Cybersecurity Framework (CSF) or ISO 27001.
- Mandatory Incident Reporting: Stricter requirements for reporting cybersecurity incidents, including timelines and the scope of information to be disclosed. This is critical for national threat intelligence and rapid response.
- Supply Chain Security: Increased scrutiny on third-party vendors and supply chain cybersecurity. Businesses are expected to ensure their vendors also meet certain security standards, recognizing that a chain is only as strong as its weakest link.
- Data Protection and Privacy: Reinforcement of data protection principles, often overlapping with existing privacy regulations (like GDPR or CCPA) but with a renewed focus on securing sensitive information from cyber threats.
- Cybersecurity Workforce Development: An implicit, and sometimes explicit, call for organizations to invest in their cybersecurity talent, through training, recruitment, and retention of skilled professionals.
- Continuous Monitoring and Assessment: Moving beyond one-time audits to continuous monitoring of systems and regular security assessments to identify vulnerabilities in real-time.
These directives reflect a proactive stance from the US government, acknowledging that cybersecurity is not a static state but an ongoing process. For businesses, this means embedding cybersecurity into the very fabric of their operations, rather than treating it as a separate IT function. The focus on US Cybersecurity Compliance is designed to foster a culture of security from the top down.
Month 1: Assessment, Planning, and Foundation Building
The first month of your 3-month compliance journey is all about understanding your current posture and laying a solid foundation for future actions. This phase is critical for defining the scope of work and allocating resources effectively for US Cybersecurity Compliance.
Week 1-2: Comprehensive Gap Analysis and Risk Assessment
Start by conducting a thorough gap analysis against the new 2026 US Cybersecurity Directives. This involves comparing your current cybersecurity policies, procedures, and technical controls with the requirements outlined in the directives. Engage a cross-functional team, including IT, legal, HR, and business unit leaders, to ensure all aspects of your operations are considered.
- Identify Applicable Directives: Determine which specific directives and regulations apply to your organization based on your industry, size, and data handling practices.
- Inventory Assets: Create a comprehensive inventory of all IT assets, including hardware, software, data, and critical systems. Understand where sensitive data resides and how it flows through your organization.
- Current State Assessment: Evaluate your existing cybersecurity controls, incident response plans, data backup strategies, and employee training programs. Document strengths and weaknesses.
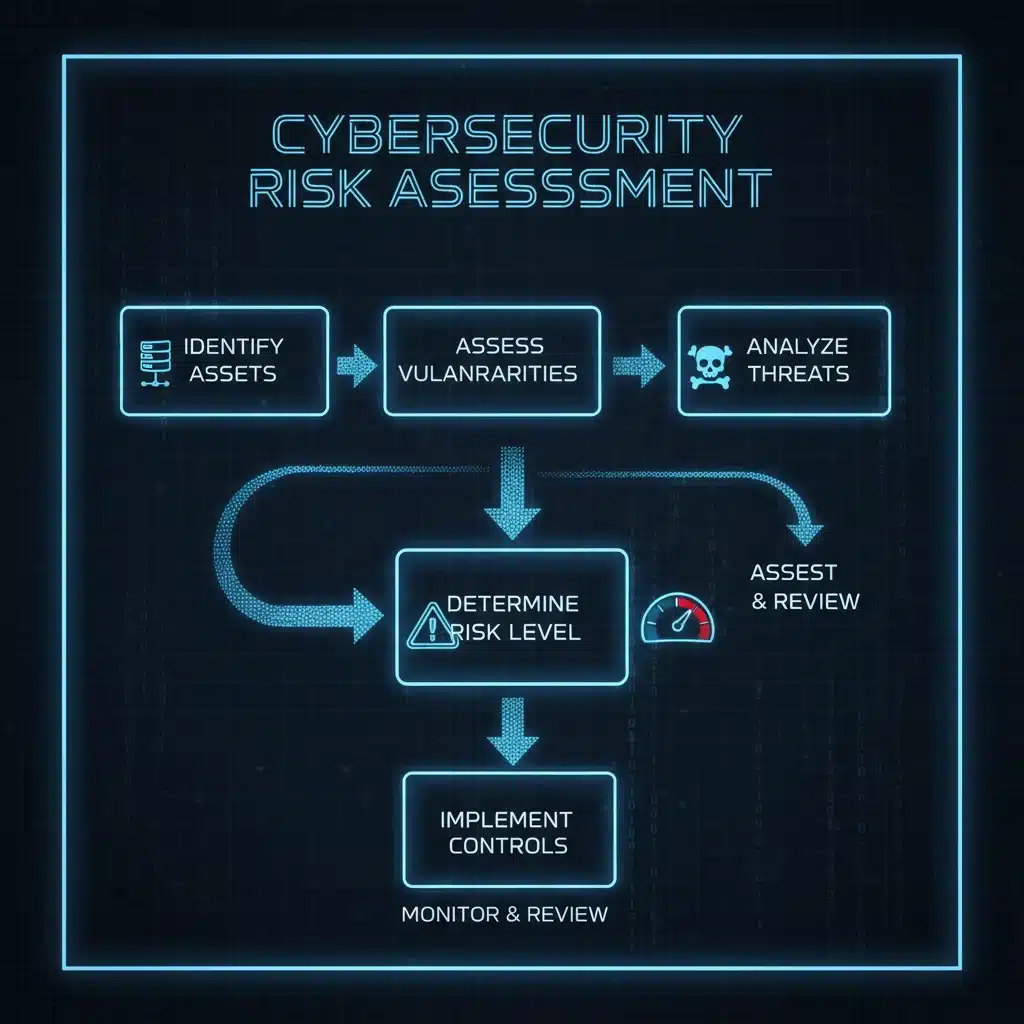
- Risk Assessment: Perform a detailed risk assessment. Identify potential threats, vulnerabilities, and the likelihood and impact of various cyber scenarios. Prioritize risks based on their potential to disrupt operations or compromise data. This is a cornerstone of effective US Cybersecurity Compliance.
Week 3-4: Develop a Detailed Compliance Roadmap and Resource Allocation
Based on your gap analysis and risk assessment, develop a detailed compliance roadmap. This plan should outline specific tasks, responsibilities, timelines, and required resources. It’s essential to be realistic about what can be achieved within the 3-month timeframe.
- Prioritize Actions: Focus on high-priority gaps and risks that pose the greatest threat or are explicitly mandated by the directives.
- Assign Ownership: Clearly assign ownership for each task to specific individuals or teams. Accountability is key to successful US Cybersecurity Compliance.
- Allocate Budget and Resources: Identify any necessary budget allocations for new tools, training, or external expertise. Secure the resources required to execute the plan.
- Policy Review and Updates: Begin reviewing and updating existing cybersecurity policies, such as acceptable use policies, data retention policies, and incident response policies, to align with the new directives.
- Legal Consultation: Consult with legal counsel specializing in cybersecurity and data privacy to ensure your interpretation and implementation of the directives are legally sound.
Month 2: Implementation and Control Enhancement
Month two is dedicated to actively implementing the changes identified in your roadmap. This involves rolling out new security controls, updating systems, and enhancing your organizational posture for US Cybersecurity Compliance.
Week 5-6: Technical Control Implementation and System Hardening
This phase focuses on the technical aspects of cybersecurity. It’s where you put your plans into action to bolster your defenses.
- Access Control Enhancements: Implement stronger access controls, including multi-factor authentication (MFA) for all critical systems and sensitive data. Review and revoke unnecessary access privileges.
- Network Security Upgrades: Enhance network segmentation, deploy advanced firewalls, intrusion detection/prevention systems (IDPS), and secure remote access solutions (e.g., VPNs).
- Endpoint Security: Ensure all endpoints (laptops, desktops, mobile devices) have up-to-date antivirus/anti-malware, endpoint detection and response (EDR) solutions, and are properly patched.
- Data Encryption: Implement encryption for data at rest and in transit, especially for sensitive and critical information, to meet US Cybersecurity Compliance standards.
- Vulnerability Management: Establish a robust vulnerability scanning and patch management program. Regularly scan your systems for vulnerabilities and apply patches promptly.
Week 7-8: Incident Response Plan Development and Testing
A well-defined and tested incident response plan is a cornerstone of the new directives. This isn’t just about having a document; it’s about having a ready and capable team.
- Develop/Update Incident Response Plan (IRP): Create or refine your IRP to include clear roles, responsibilities, communication protocols (internal and external), and procedures for detection, containment, eradication, recovery, and post-incident analysis.
- Mandatory Reporting Procedures: Integrate the new mandatory incident reporting requirements into your IRP, including specific timelines and contact points for regulatory bodies.
- Tabletop Exercises: Conduct tabletop exercises or simulations to test your IRP. Involve key stakeholders to identify weaknesses and refine procedures. This practical testing is vital for effective US Cybersecurity Compliance.
- Backup and Disaster Recovery: Verify and test your data backup and disaster recovery plans. Ensure that critical data can be restored quickly and reliably in the event of a cyberattack.
Month 3: Training, Monitoring, and Continuous Improvement
The final month is dedicated to solidifying your compliance efforts through training, establishing continuous monitoring, and preparing for ongoing maintenance. This ensures that your US Cybersecurity Compliance is sustainable.
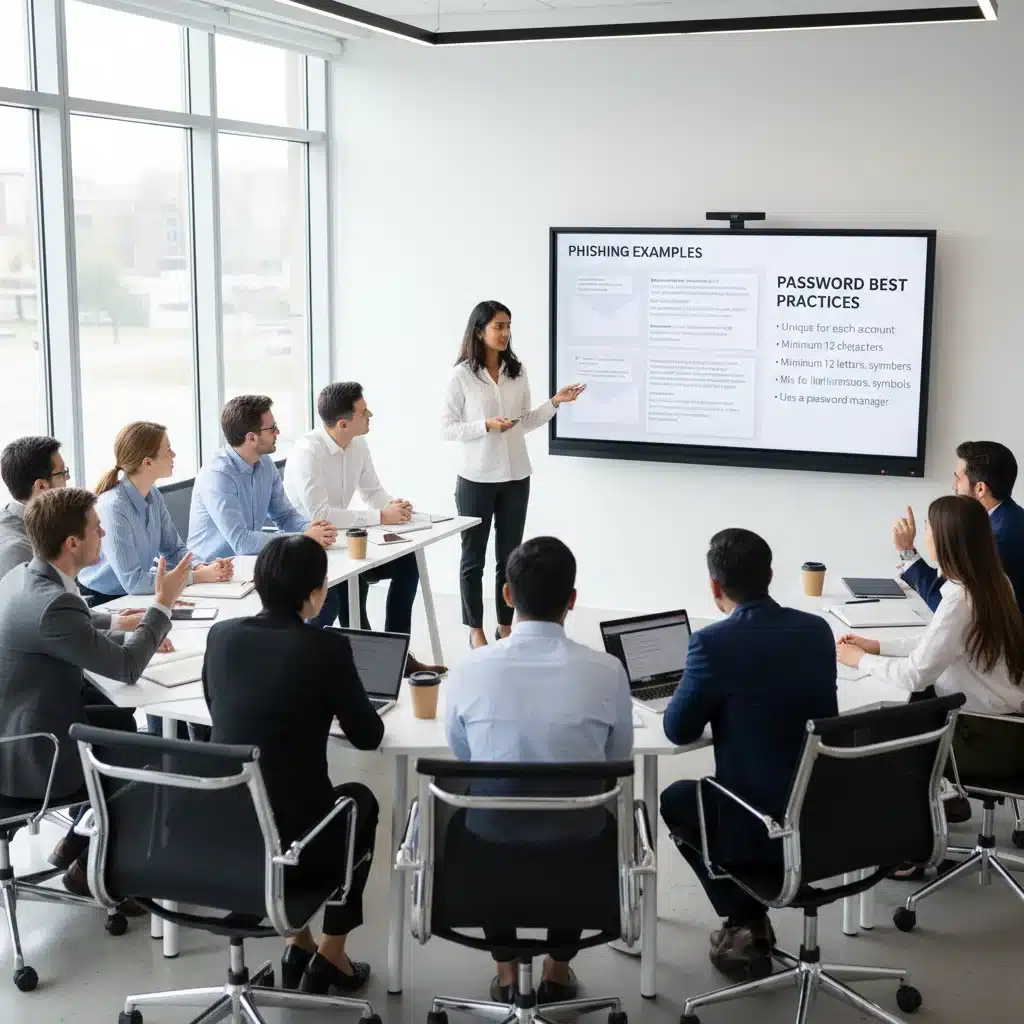
Week 9-10: Employee Training and Awareness Programs
Human error remains a leading cause of security breaches. Educating your workforce is paramount to building a strong security posture.
- Cybersecurity Awareness Training: Implement mandatory, comprehensive cybersecurity awareness training for all employees. Topics should include phishing recognition, strong password practices, data handling best practices, and reporting suspicious activities.
- Role-Specific Training: Provide specialized training for employees with elevated access privileges or those handling sensitive data, focusing on their specific responsibilities in maintaining security.
- Phishing Simulations: Conduct regular phishing simulations to test employee vigilance and reinforce training. Provide immediate feedback and additional training for those who fall for simulations.
- Policy Communication: Clearly communicate updated cybersecurity policies and procedures to all employees, ensuring they understand their role in maintaining US Cybersecurity Compliance.
Week 11-12: Continuous Monitoring, Auditing, and Documentation
Compliance is not a one-time event. It requires continuous vigilance and a commitment to ongoing improvement. This is the final push to demonstrate robust US Cybersecurity Compliance.
- Implement Security Information and Event Management (SIEM): Deploy or enhance SIEM solutions to centralize security logging, monitor for suspicious activities, and provide real-time alerts.
- Regular Internal Audits: Conduct regular internal audits of your cybersecurity controls and processes to ensure they remain effective and aligned with the directives.
- Third-Party Vendor Management: Review and strengthen your third-party vendor management program. Ensure that your contracts include appropriate cybersecurity clauses and that vendors meet your security requirements. Conduct due diligence on new vendors.
- Documentation and Record-Keeping: Meticulously document all compliance efforts, including policies, procedures, training records, incident reports, and audit results. This documentation will be crucial for demonstrating US Cybersecurity Compliance to regulators.
- Establish Metrics and Reporting: Define key performance indicators (KPIs) and metrics to track your cybersecurity posture and compliance status. Establish a regular reporting mechanism to senior management and the board.
- Prepare for External Audits: If applicable, prepare for potential external audits or assessments by regulatory bodies. Ensure all documentation is readily available and your team is prepared to answer questions.
Beyond 3 Months: Sustaining US Cybersecurity Compliance
Achieving compliance within three months is a significant accomplishment, but the journey doesn’t end there. Cybersecurity is a dynamic field, and directives will continue to evolve. Sustaining US Cybersecurity Compliance requires a commitment to ongoing vigilance and adaptation.
Continuous Improvement Loop
Implement a continuous improvement loop for your cybersecurity program. This involves:
- Regular Review: Periodically review your risk assessments, policies, and controls to ensure they remain relevant and effective against emerging threats.
- Threat Intelligence Integration: Stay informed about the latest cyber threats and vulnerabilities. Integrate threat intelligence into your security operations to proactively defend against new attacks.
- Technology Updates: Keep your security technologies up-to-date. Invest in new solutions as needed to address evolving risks and compliance requirements.
- Employee Refreshers: Conduct regular refresher training for employees to keep cybersecurity awareness at the forefront of their minds.
- Adapt to New Regulations: Monitor for new or updated directives and regulations. Proactively adjust your compliance strategy to incorporate any changes.
Building a Culture of Security
Ultimately, the goal is to embed cybersecurity into your organizational culture. This means:
- Leadership Buy-in: Ensure that cybersecurity is a priority for senior leadership and the board. Their support is crucial for resource allocation and cultural change.
- Employee Empowerment: Empower employees to be the first line of defense. Encourage them to report suspicious activities without fear of reprisal.
- Cross-functional Collaboration: Foster collaboration between IT, legal, HR, and business units on cybersecurity matters.
- Transparency: Be transparent about cybersecurity risks and incidents, both internally and externally (where appropriate), to build trust and accountability.
The Strategic Advantages of Proactive US Cybersecurity Compliance
While compliance might seem like a burden, viewing it solely as a checklist misses the broader strategic advantages. Proactive US Cybersecurity Compliance can:
- Enhance Customer Trust: Demonstrating a strong commitment to data protection builds trust with customers, which can be a significant competitive differentiator.
- Improve Business Resilience: A robust cybersecurity posture minimizes the risk of costly breaches and operational disruptions, ensuring business continuity.
- Attract and Retain Talent: Employees prefer working for organizations that prioritize security and protect their data.
- Reduce Insurance Premiums: Strong cybersecurity controls can lead to lower cybersecurity insurance premiums.
- Foster Innovation: A secure environment allows businesses to innovate and adopt new technologies with greater confidence, knowing their core assets are protected.
Conclusion
The 2026 US Cybersecurity Directives represent a pivotal moment for businesses. While the 3-month compliance window presents a challenge, it’s also an opportunity to significantly enhance your organization’s security posture and build lasting resilience. By meticulously following this guide – from initial assessment and planning to technical implementation, employee training, and continuous monitoring – your business can confidently navigate these new requirements. Remember, US Cybersecurity Compliance is not merely about avoiding penalties; it’s about safeguarding your assets, protecting your customers, and securing your future in an increasingly digital world. Start your journey today, and transform compliance into a strategic advantage.