2026 Federal Data Privacy Regulations: A 6-Month Action Plan for Businesses
Anúncios
Understanding the 2026 Federal Data Privacy Regulations: A 6-Month Action Plan for Businesses
The digital landscape is constantly evolving, and with it, the imperative for robust data privacy. Businesses worldwide are grappling with an increasingly complex web of regulations, and the United States is no exception. As we inch closer to 2026, the impending federal data privacy regulations stand as a significant milestone, promising to reshape how organizations collect, process, store, and share personal information. This isn’t just another set of rules; it represents a fundamental shift in accountability and consumer rights, demanding a proactive and strategic response from every enterprise, regardless of size or sector.
Anúncios
The exact contours of the 2026 federal data privacy regulations are still taking shape, but the direction is clear: increased transparency, stronger individual control over personal data, and more stringent requirements for data security and breach notification. For businesses, this translates into a critical need for comprehensive preparation. Waiting until the last minute is not an option; the potential penalties for non-compliance, coupled with the irreparable damage to brand reputation, are simply too high.
This article serves as your indispensable guide, offering a practical, time-sensitive 6-month action plan designed to help your business navigate the complexities of these new federal data privacy mandates. We’ll break down the critical steps you need to take, month by month, to ensure your organization is not just compliant, but also poised to thrive in a privacy-first world. From initial data mapping to employee training and technological overhauls, we’ll cover the essential components of a successful compliance strategy.
The goal is not only to avoid penalties but to build trust with your customers. In an era where data breaches are common and consumer skepticism is high, demonstrating a genuine commitment to data privacy can be a powerful differentiator. Let’s embark on this journey together, transforming what might seem like a daunting challenge into a strategic opportunity for growth and enhanced customer loyalty.
Anúncios
Understanding the Landscape: What to Expect from 2026 Federal Data Privacy
Before diving into the action plan, it’s crucial to grasp the potential scope and impact of the 2026 federal data privacy regulations. While specific details may evolve, general principles are likely to align with existing comprehensive privacy laws like Europe’s GDPR and California’s CCPA. These typically include:
- Expanded Definition of Personal Data: Expect a broad interpretation of what constitutes ‘personal data,’ encompassing not just names and addresses, but also IP addresses, cookies, biometric data, and more.
- Enhanced Consumer Rights: Individuals will likely gain stronger rights to access, correct, delete, and port their personal data. The right to opt-out of data sales and targeted advertising will also be a core component.
- Data Minimization and Purpose Limitation: Businesses will be expected to collect only the data necessary for a specific, stated purpose and to use it only for that purpose.
- Increased Transparency: Clear, concise, and easily accessible privacy notices will be mandatory, informing consumers about data collection practices, purposes, and their rights.
- Data Protection by Design and Default: Privacy considerations must be embedded into the design of systems and business practices from the outset, rather than being an afterthought.
- Vendor Management Obligations: Businesses will be held accountable for the data privacy practices of their third-party vendors and service providers.
- Data Breach Notification Requirements: Strict timelines and procedures for notifying affected individuals and regulatory authorities in the event of a data breach.
- Designated Data Protection Officers (DPOs): Certain organizations, particularly those processing large volumes of sensitive data, may be required to appoint a DPO.
- Stricter Enforcement and Penalties: Expect significant fines for non-compliance, alongside the potential for private rights of action.
The overarching theme is a shift towards greater accountability for businesses and increased control for individuals over their digital footprint. Preparing for these changes requires a holistic approach, touching upon legal, technical, operational, and cultural aspects of your organization.
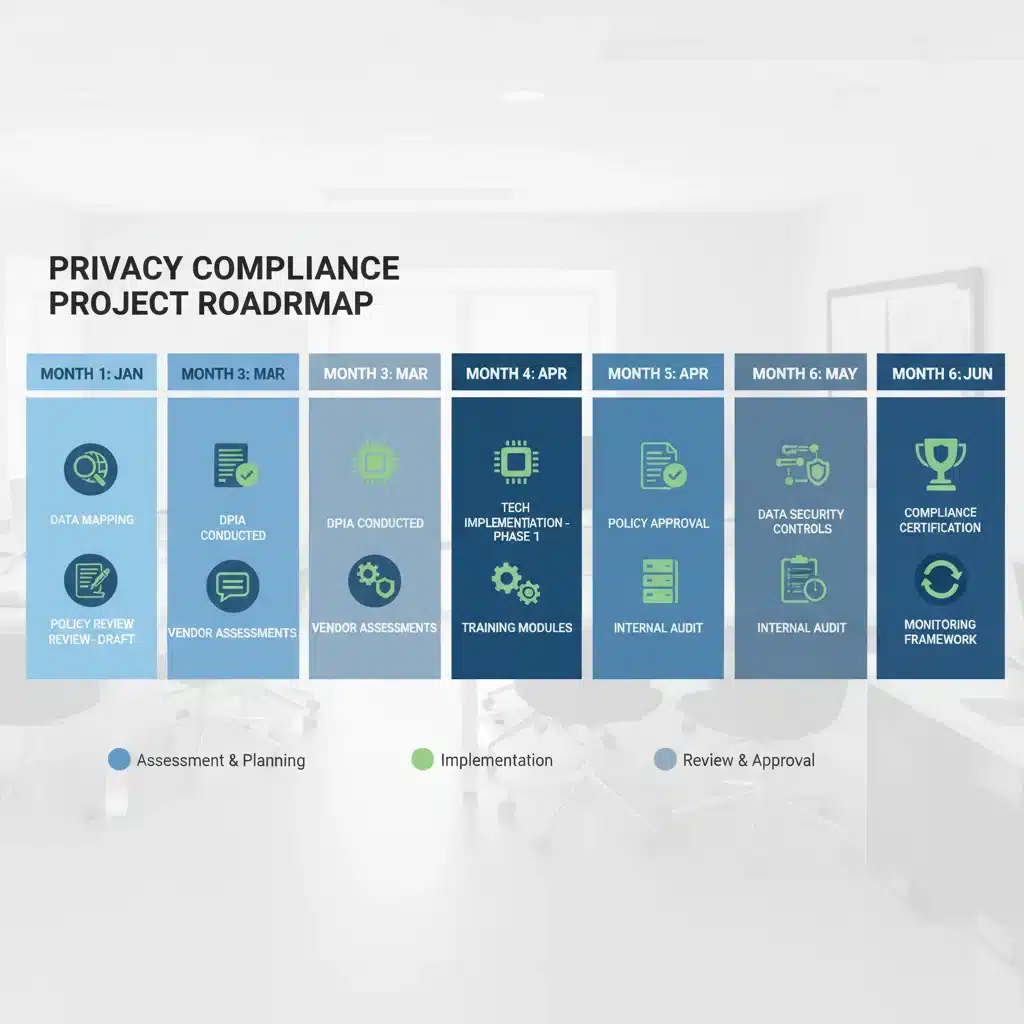
The 6-Month Action Plan: Your Roadmap to Federal Data Privacy Compliance
This phased approach allows your business to systematically address the various facets of the new federal data privacy regulations, minimizing disruption and maximizing effectiveness. Each month builds upon the previous one, ensuring a comprehensive and robust compliance framework.
Month 1: Discovery and Assessment – Laying the Foundation for Federal Data Privacy
The first month is all about understanding your current data landscape. You can’t protect what you don’t know you have. This phase is critical for establishing a baseline for your compliance efforts.
- Form a Dedicated Privacy Task Force: Assemble a cross-functional team including representatives from legal, IT, marketing, HR, and operations. Assign a project lead responsible for overseeing the entire compliance initiative. This team will be central to your success in navigating the new federal data privacy requirements.
- Conduct a Data Inventory and Mapping Exercise: This is arguably the most crucial step. Identify all personal data your organization collects, processes, stores, and transmits. For each data point, document:
- What data is collected?
- Why is it collected (purpose)?
- How is it collected (sources)?
- Where is it stored (systems, databases, cloud services)?
- Who has access to it?
- With whom is it shared (third-party vendors, partners)?
- How long is it retained?
- What are the legal bases for processing this data?
- Review Existing Privacy Policies and Procedures: Compare your current internal policies (e.g., data retention, access control, incident response) and external-facing privacy notices against anticipated federal data privacy principles. Identify gaps and areas requiring significant updates.
- Assess Current Data Security Measures: Evaluate your existing cybersecurity framework. Are your data encryption, access controls, intrusion detection systems, and vulnerability management robust enough to protect the personal data you hold? Consider conducting a security audit.
- Identify Key Stakeholders and Their Roles: Determine who in your organization will be responsible for specific aspects of privacy compliance moving forward. This clarity is essential for effective implementation of the federal data privacy framework.
Utilize data discovery tools if your organization handles a large volume of data. This mapping will provide a clear picture of your data flows and highlight areas of risk and non-compliance with future federal data privacy rules.
Month 2: Gap Analysis and Risk Assessment – Pinpointing Vulnerabilities
With a clear understanding of your data landscape, month two focuses on identifying where your current practices fall short of the anticipated federal data privacy requirements and assessing the associated risks.
- Perform a Detailed Gap Analysis: Based on your data inventory and review of existing policies, identify specific discrepancies between your current state and the expected 2026 federal data privacy regulations. This includes gaps in data collection practices, consent mechanisms, data subject request handling, and data security.
- Conduct a Data Protection Impact Assessment (DPIA) / Privacy Impact Assessment (PIA): For high-risk data processing activities (e.g., new technologies, large-scale processing of sensitive data, international data transfers), conduct a formal DPIA. This helps identify and mitigate privacy risks before they materialize, a key tenet of federal data privacy.
- Prioritize Risks: Not all gaps are created equal. Prioritize identified risks based on their potential impact (e.g., financial penalties, reputational damage, operational disruption) and likelihood. This will guide your remediation efforts.
- Review Third-Party Vendor Contracts: Scrutinize contracts with all vendors who process personal data on your behalf. Ensure they include appropriate data protection clauses, data processing agreements (DPAs), and audit rights that align with upcoming federal data privacy standards.
- Legal Counsel Consultation: Engage legal counsel specializing in data privacy to interpret the nuances of the emerging federal data privacy regulations and advise on specific compliance challenges.
Month 3: Policy Development and Updates – Crafting Your New Federal Data Privacy Framework
Month three is dedicated to revising and creating the necessary documentation and policies to meet the impending federal data privacy standards.
- Develop/Update Privacy Policy and Notices: Draft clear, transparent, and comprehensive privacy policies for your website, apps, and other data collection points. Ensure they explicitly inform users about their rights under the new federal data privacy regulations and how to exercise them.
- Establish Data Subject Request (DSR) Procedures: Create robust, documented processes for handling requests from individuals regarding their data (access, correction, deletion, portability, opt-out). This includes defining roles, responsibilities, timelines, and verification methods.
- Revise Internal Data Handling Policies: Update internal policies on data collection, use, storage, retention, and disposal to reflect the principles of data minimization, purpose limitation, and accountability mandated by federal data privacy.
- Implement Data Breach Response Plan Updates: Ensure your incident response plan includes specific procedures for identifying, assessing, and reporting data breaches in accordance with the strict notification requirements of the new federal data privacy regulations.
- Update Vendor Agreements: Amend existing contracts with third-party processors to incorporate necessary data protection clauses and ensure they are also compliant with the new federal data privacy framework.
Month 4: Technology and Infrastructure Adjustments – Enabling Federal Data Privacy Compliance
This month focuses on the technical adjustments required to support your new federal data privacy policies and procedures.
- Implement Consent Management Platforms (CMPs): Deploy or upgrade CMPs to effectively manage user consent preferences for cookies, marketing communications, and other data processing activities, aligning with the opt-in/opt-out requirements of federal data privacy.
- Enhance Data Access and Deletion Tools: Invest in or develop tools that allow for efficient location, access, modification, and deletion of personal data across all your systems in response to DSRs.
- Strengthen Data Security Controls: Implement additional security measures identified during your risk assessment. This could include enhanced encryption, multi-factor authentication, data loss prevention (DLP) solutions, and regular security audits.
- Automate Data Retention Policies: Implement systems that automatically enforce data retention schedules, ensuring personal data is not kept longer than necessary, a core principle of federal data privacy.
- Review and Update IT Infrastructure: Assess whether your current IT infrastructure can adequately support the new privacy requirements. This might involve cloud security enhancements, network segmentation, and secure data transfer protocols.
Month 5: Training and Awareness – Cultivating a Culture of Federal Data Privacy
Technology and policies are only as effective as the people who use them. Month five is dedicated to ensuring your entire organization understands and embraces their role in upholding federal data privacy.
- Develop and Deliver Comprehensive Employee Training: Conduct mandatory training sessions for all employees who handle personal data. Tailor training content to different roles and responsibilities (e.g., marketing, sales, HR, IT). Cover topics such as:
- What constitutes personal data.
- The new federal data privacy rights of individuals.
- How to identify and handle DSRs.
- Data minimization principles.
- Data security best practices (e.g., strong passwords, phishing awareness).
- Internal reporting procedures for privacy incidents and breaches.
- Create Awareness Campaigns: Use internal communications (e.g., newsletters, posters, intranet announcements) to continuously reinforce the importance of data privacy and the impact of the new federal data privacy regulations.
- Train Key Personnel on DSR Handling: Provide specialized, in-depth training for individuals responsible for processing data subject requests to ensure efficiency and compliance.
- Establish a Culture of Privacy: Emphasize that data privacy is a shared responsibility, not just an IT or legal issue. Foster an environment where employees feel empowered to report potential privacy risks and understand their role in protecting customer data.
Month 6: Testing, Review, and Continuous Improvement – Sustaining Federal Data Privacy Compliance
The final month before the 2026 deadline is about validation, refinement, and establishing a framework for ongoing compliance with federal data privacy regulations.
- Conduct Internal Audits and Testing: Perform mock data subject requests and simulated data breaches to test the effectiveness of your new policies, procedures, and technical controls. Identify any weaknesses and make immediate adjustments.
- Review and Finalize Documentation: Ensure all privacy policies, procedures, and records of processing activities are up-to-date, accurate, and readily accessible. This documentation will be crucial for demonstrating compliance to regulators.
- Establish a Compliance Monitoring Program: Implement ongoing monitoring mechanisms to ensure continuous adherence to the federal data privacy regulations. This includes regular reviews of data processing activities, security logs, and vendor compliance.
- Appoint a Data Protection Officer (DPO) or Privacy Lead: If required by the regulations or deemed beneficial for your organization, formally appoint a DPO or a dedicated privacy lead to oversee ongoing compliance efforts.
- Prepare for Regulatory Scrutiny: Understand the enforcement mechanisms and potential penalties associated with the new federal data privacy regulations. Ensure your organization is prepared to respond to inquiries from regulatory bodies.
- Plan for Ongoing Training and Updates: Data privacy is not a one-time project. Develop a plan for regular employee training refreshers and for staying abreast of future amendments or clarifications to the federal data privacy regulations.
Beyond Compliance: The Strategic Advantage of Proactive Federal Data Privacy
While the primary driver for this 6-month action plan is compliance with the 2026 federal data privacy regulations, the benefits of a robust privacy framework extend far beyond avoiding penalties. Proactive data privacy management can yield significant strategic advantages:
- Enhanced Customer Trust and Loyalty: Consumers are increasingly conscious of how their data is handled. Demonstrating a strong commitment to privacy builds trust, which can translate into increased customer loyalty and brand preference.
- Improved Data Quality: The process of data mapping and minimization often leads to a cleaner, more accurate, and more useful dataset, enabling better business intelligence and decision-making.
- Reduced Risk of Data Breaches: Strengthening your data security posture as part of privacy compliance naturally reduces your vulnerability to costly and damaging data breaches.
- Streamlined Operations: Well-defined data handling policies and automated processes for DSRs can lead to more efficient and organized internal operations.
- Competitive Differentiation: In a crowded marketplace, a strong privacy stance can differentiate your brand, attracting privacy-conscious consumers and partners.
- Preparedness for Future Regulations: Investing in a comprehensive privacy program now will put your business in a much stronger position to adapt to future privacy laws and amendments, reducing future compliance burdens.
Challenges and Considerations for Federal Data Privacy Implementation
Implementing a comprehensive federal data privacy compliance program is not without its challenges. Businesses should be prepared for:
- Resource Allocation: Compliance requires significant investment in time, personnel, and technology.
- Data Silos and Legacy Systems: Older systems and fragmented data storage can make data mapping and DSR handling particularly complex.
- Organizational Buy-in: Gaining full commitment from leadership and all departments is crucial for success.
- Evolving Regulatory Interpretations: The exact interpretation and enforcement of the new federal data privacy laws may evolve over time, requiring continuous adaptation.
- Managing Third-Party Risk: Ensuring all vendors and partners are compliant adds another layer of complexity.
Overcoming these challenges requires clear communication, strong project management, and a willingness to adapt. Focus on incremental progress and celebrate small victories to maintain momentum.
Conclusion: Embracing a Privacy-First Future with Federal Data Privacy
The 2026 federal data privacy regulations represent a pivotal moment for businesses operating in the United States. While the journey to full compliance may seem arduous, approaching it with a structured, phased action plan can transform this regulatory requirement into a strategic opportunity. By diligently following the steps outlined in this 6-month roadmap, your organization can not only mitigate legal and financial risks but also cultivate deeper trust with your customers, enhance operational efficiency, and gain a competitive edge in an increasingly privacy-aware world.
Remember, data privacy is not a destination but a continuous journey. The principles of transparency, accountability, and individual control should become ingrained in your organizational culture. By embracing these changes now, your business will be well-prepared to navigate the evolving digital landscape and thrive in the privacy-first future that the 2026 federal data privacy regulations herald.
Start today. Your future success depends on it.